Disk Encryption
Full Disk Encryption on Linux Explained by KaliLinux.net
KaliLinux.net explains full disk encryption on Linux using LUKS, Kali installer choices, passphrase risks, header backup, and encrypted lab setup.
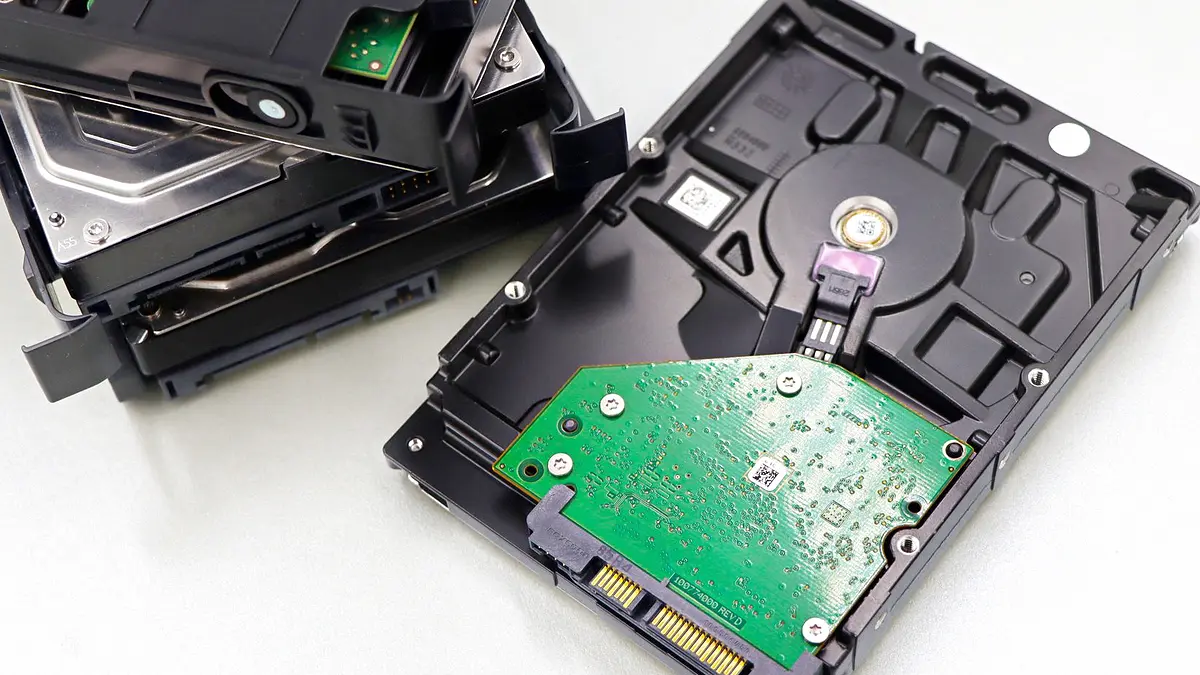
Setting up full disk encryption usually gets treated like a mere checkbox during installation. At KaliLinux.net, we view it as a non-negotiable baseline for any laptop, field device, or USB persistence drive carrying client scoping files, lab notes, or packet captures. The official Kali installation documentation covers the encrypted LVM path if you need the installer walkthrough. Keep in mind that encryption never makes Kali invulnerable. It simply protects data at rest when powered down, forcing the machine to require a passphrase before the OS boots up.
What LUKS actually protects
LUKS, short for Linux Unified Key Setup, is not the actual encryption algorithm. It sits right on top of dm-crypt inside the kernel to handle keys, metadata, and passphrases. When you select encrypted LVM in Kali, LUKS does the heavy lifting. The modern LUKS2 specification stores header data in JSON and defaults to Argon2 for passphrase hashing.
Argon2 is memory-hard, making offline brute-force attacks against a stolen drive painfully slow. Still, encryption only covers data at rest. It will not hide runtime activity, block malware running with root privileges, or protect against an attacker who snatches an already unlocked laptop. Threat modeling matters here. If someone grabs your machine while it is running with an open session, your encryption boundary has already failed.

Kali install choices and passphrase reality
Guided partitioning in the Kali installer makes setting up encrypted LVM straightforward, but the passphrase remains the weakest link. Pick something long and randomized rather than a predictable dictionary word with a digit tagged on the end.
LUKS supports multiple key slots, so you can keep a secondary recovery passphrase stored seperately. Many testers also rely on LUKS-encrypted persistence on live USB drives to store session artifacts between assessments.
Just remember: if you lose that passphrase, your data is gone for good. There is no backdoor. While a header backup helps recover from accidental header corruption, it won’t bypass lost credentials. Always run cryptsetup luksHeaderBackup before touching key slots, and store that backup file offline.
Lab testing and common mistakes
Always test your disk configuation in a virtual enviroment before wiping a production field laptop. Encrypting older hardware can alter boot flows, occasionally requiring manual adjustments in UEFI or BIOS settings to point to the proper boot target.
Another frequent oversight involves unencrypted swap space. Encrypting root while leaving swap exposed means sensitive memory artifacts get written to disk in plain text. Kali’s guided encrypted LVM typically bundles swap inside the mapped volume, but manual partitioning schemes can easily leave it unencrypted. Run lsblk or cryptsetup status to verify your swap resides on the encrypted container.

Full disk encryption is recomended for every Kali installation taken into the field. It is not some obscure feature reserved for paranoid setups; it is standard tradecraft for protecting client data, captured traffic, and assessment logs. Test the workflow, preserve your header backups, and use a passphrase robust enough to withstand offline attacks.
Pertanyaan yang sering diajukan
What is full disk encryption on Linux?
Does Kali Linux support full disk encryption during installation?
Does encryption protect a running Kali machine?
Can I recover data if I forget my LUKS passphrase?
Situs tetap hidup saat diserang, pindah domain dalam menit saat diblokir
Trafik disaring berlapis sebelum menyentuh server. Dua server: kalau satu tumbang, panel otomatis memindahkan ke server kedua.
- Penyaringan berlapis
- 2 server, auto-pindah
- Rp 7,5 jt/bln · 10 domain